security
ASP.NET Core and .NET Security Articles, Tutorials & News
ASP.NET Core and .NET Security articles, tutorials, and news from the DotNetNews archive.
547 articles Updated
This DotNetNews topic collects ASP.NET Core security material from the daily archive. ASP.NET Core and .NET Security sits in the ASP.NET Core and broader Microsoft web stack that most C# services use. The page is for people who already ship C# and need a faster way to find relevant posts.
Expect publisher tutorials, release notes, architecture write-ups, and field notes linked from DotNetNews issues. Start here is a short editorial shortlist for ASP.NET Core and .NET Security; the archive list is chronological and larger. Nothing here claims every article was production-tested by the editors.
Recurring subtopics in recent issues include ASP.NET Core security, .NET security, secure coding C#, and ASP.NET Core hardening. Secondary angles such as ASP.NET Core security and .NET security appear when the archive actually covered them. Related hubs such as ASP.NET Core Authentication and ASP.NET Core Authorization cover adjacent problems.
Each card points at the original publisher URL and the DotNetNews issue that carried it, so you can read the article in context or jump straight to the source.
Start here
Editor picks for Security
-

Implementing Passkey Authentication in ASP.NET Core Applications
C# Corner Issue #502
Passkeys keep moving from nice-to-have to baseline. Good starter piece for WebAuthn in ASP.NET Core.
-

OWASP Top 10 for .NET Developers - Part 8: Preventing Software and Data Integrity Failures
Medium Issue #497
A worthwhile security reminder that clean scans and passing tests do not cover supply-chain and integrity failure risks.
-

Why and When We Need to Use [CustomAuthorize] in ASP.NET
Medium Issue #497
Custom authorization is easy to overuse, so the "when" is the important part of this discussion.
-

How to Implement Passkey Authentication in ASP.NET Core Applications
C# Corner Issue #491
Implement secure passkey authentication in ASP.NET Core apps.
-
How Hidden Security Vulnerabilities Turn Into Business-Critical Incidents in Modern Applications
Medium Issue #490
Less framework-specific, but the business framing around hidden vulnerabilities and incident cost is still relevant for engineering leads.
-
Elsa 3.8 Preview: Secrets, State Machines, and a Security Hardening Pass
Medium Issue #489
Worth a skim if Elsa is on your radar and you care about security posture.
-

Building for the agentic web with .NET 11
YouTube Issue #472
Agentic web apps on .NET 11 shift from request-response to autonomous agent patterns.
-
Stop prompt injection from hijacking your agent, new security capabilities now released within Agent Framework
Microsoft Dev Blogs Issue #465
Prompt injection is still the biggest agent risk, so I'm glad to see more concrete platform defenses landing here.
Archive
Page 1 of 22
Newest first
-
How to Revoke a JWT Before It Expires
Milan's .NET Weekly Issue #574
ASP.NET Core validates a JWT by its signature and expiry, so a stolen token keeps working after the user changes their password.
-

How Long Should You Keep Closed Dependabot Alerts?
C# Corner - Riya Patel Issue #574
-
How to Test Post-Quantum Key Exchange APIs in .NET 11
C# Corner Issue #573
Learn how to test ML-KEM key encapsulation and decapsulation in .NET 11, including shared-secret verification, key import, invalid-input handling, and cross-platform support.
-

NVIDIA Launches Open Agent Safety Platform for AI Agents
C# Corner - Mahesh Chand Issue #572
-
Stop shipping the sops binary in your .NET images
Medium Issue #572
SOPS is a good way to keep secrets in git. It encrypts the values in a YAML, JSON, dotenv, INI or binary file while leaving the keys…
-
How to Secure File Uploads in ASP.NET Core by Checking File Signatures
C# Corner Issue #572
Learn how to secure ASP.NET Core file uploads by validating file signatures, enforcing allowlists and size limits, and safely handling uploaded files.
-
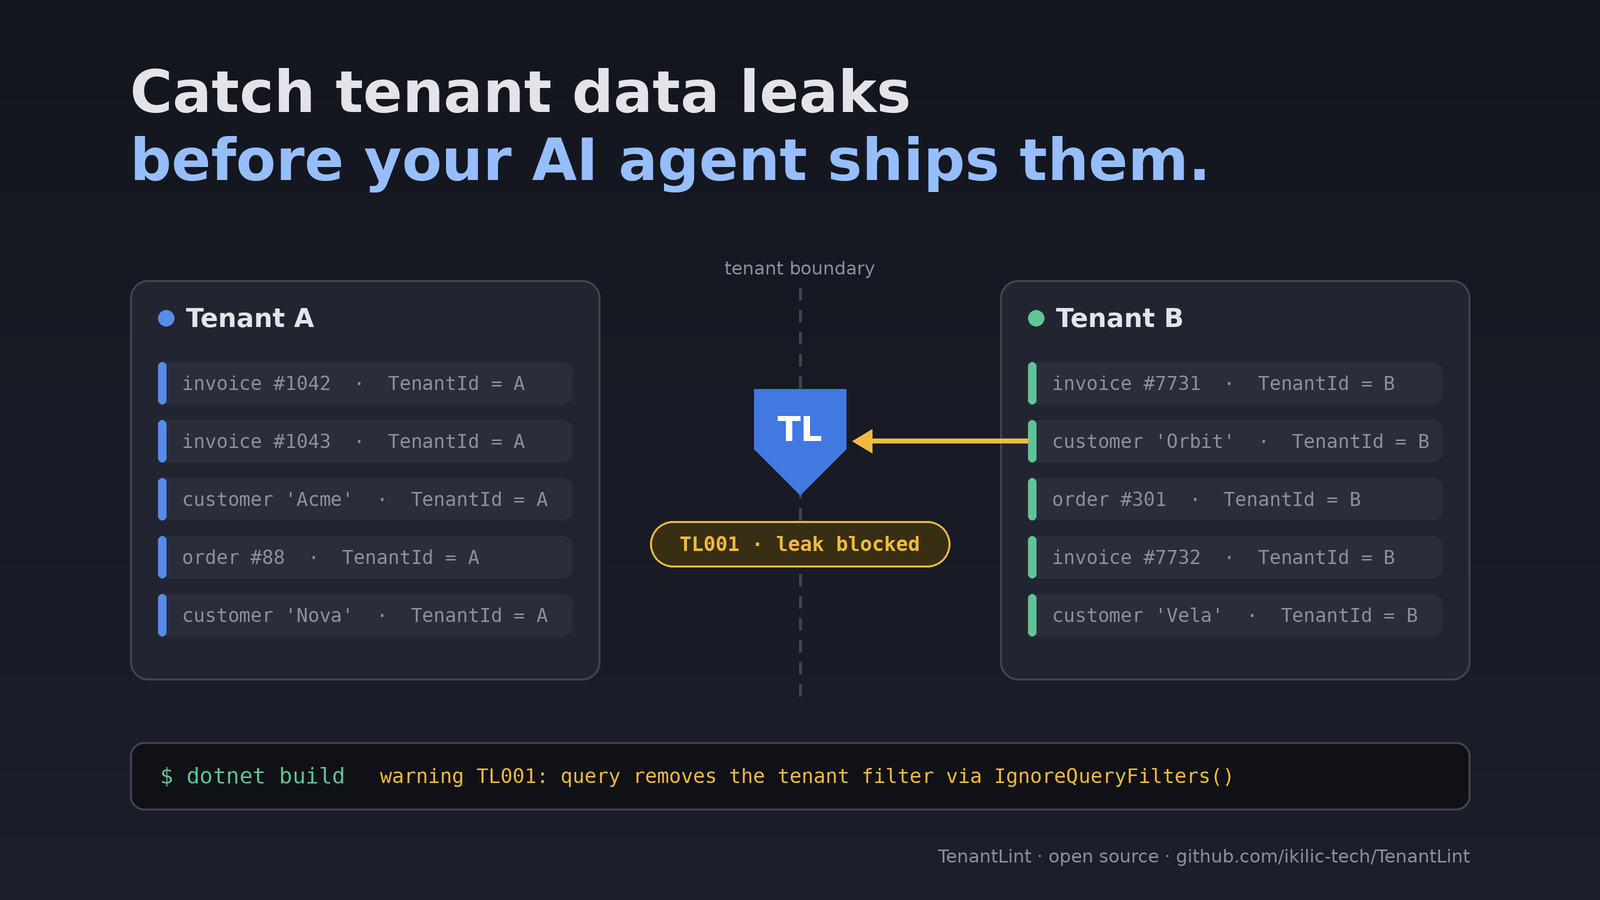
Your AI coding agent can leak one customer’s data to another — and every test will still pass
Medium Issue #571
I built TenantLint, an open-source Roslyn analyzer that catches cross-tenant data leaks in .NET at build time: in your IDE, in CI, and…
-
How to Add Rate Limiting to ASP.NET Core APIs
C# Corner Issue #570
Learn how to configure and apply ASP.NET Core rate limiting policies, choose limiter algorithms, and return HTTP 429 responses for excessive API requests.
-
GitHub Is Changing Dependabot Alert Retention: What Gets Deleted?
C# Corner - Riya Patel Issue #570
-
How to Secure File Uploads in ASP.NET Core by Checking File Signatures
C# Corner Issue #569
Learn how to secure ASP.NET Core file uploads by validating file signatures, enforcing size limits, and safely storing uploaded files.
-

How to Build a Provably Fair Verification Tool in C# with SHA-256 and HMAC-SHA256
C# Corner - Jutsu Casino Issue #568
-
Restoring Readable Crash Logs from Obfuscated .NET Builds: A Field Guide to Symbol Map Deobfuscation
C# Corner - Rustem soft Issue #568
Learn how to securely store .NET obfuscation maps and use them to restore readable C# stack traces from production crash logs.
-
Secure File Uploads in ASP.NET Core: Validate File Signatures, Not Just Extensions
C# Corner - Ananya Desai Issue #566
Learn how to secure ASP.NET Core file uploads by validating extensions and file signatures, enforcing size limits, and safely storing uploaded files.
-
Verify Webhook Signatures and Reject Replayed Requests
C# Corner - Saurav Kumar Issue #566
Learn how to verify HMAC webhook signatures from raw request bodies and prevent replayed requests with timestamps, event IDs, and idempotent processing in ASP.NET Core.
-

AI Security Agents: How GitHub Found 24 Android Vulnerabilities
C# Corner - Nidhi Sharma Issue #566
-
How to Add Rate Limiting to ASP.NET Core APIs
C# Corner Issue #565
Configure ASP.NET Core API rate limiting with built-in middleware, endpoint policies, HTTP 429 responses, and fixed, sliding, token bucket, and concurrency limiters.
-
How to Add Passkey Login to an ASP.NET Core Application
C# Corner Issue #565
Learn how to add passkey login to ASP.NET Core using WebAuthn, including credential storage, registration challenges, authentication verification, and security considerations.
-
How to Change JWT Signing Keys Without Breaking Existing API Clients
C# Corner Issue #565
Learn how to rotate JWT signing keys in ASP.NET Core while validating tokens signed with old and new keys during a secure transition.
-
GitHub Adds More CVE Data to the Security Advisory API
C# Corner - Aarav Patel Issue #565
-

Secure Password Hashing and Verification in ASP.NET Core
C# Corner - Sardar Mudassar Ali Khan Issue #564
-
How to wipe Android phone before trade in or selling?
Microsoft Tech Community - Jokse Issue #564
Before trading in or selling my Android. I want to make sure that my personal messages and other private information are completely removed from the device. I have been researching how to wipe Android...
-
Your code reads secrets from Vault. What do you test it against?
Medium - Ferhat Talha BULANIK Issue #563
I wrote a small package that starts and stops a real Vault from inside .NET
-

Complete Guide: Securing MS SQL Server on Ubuntu with Fail2Ban
C# Corner - Sardar Mudassar Ali Khan Issue #562
-
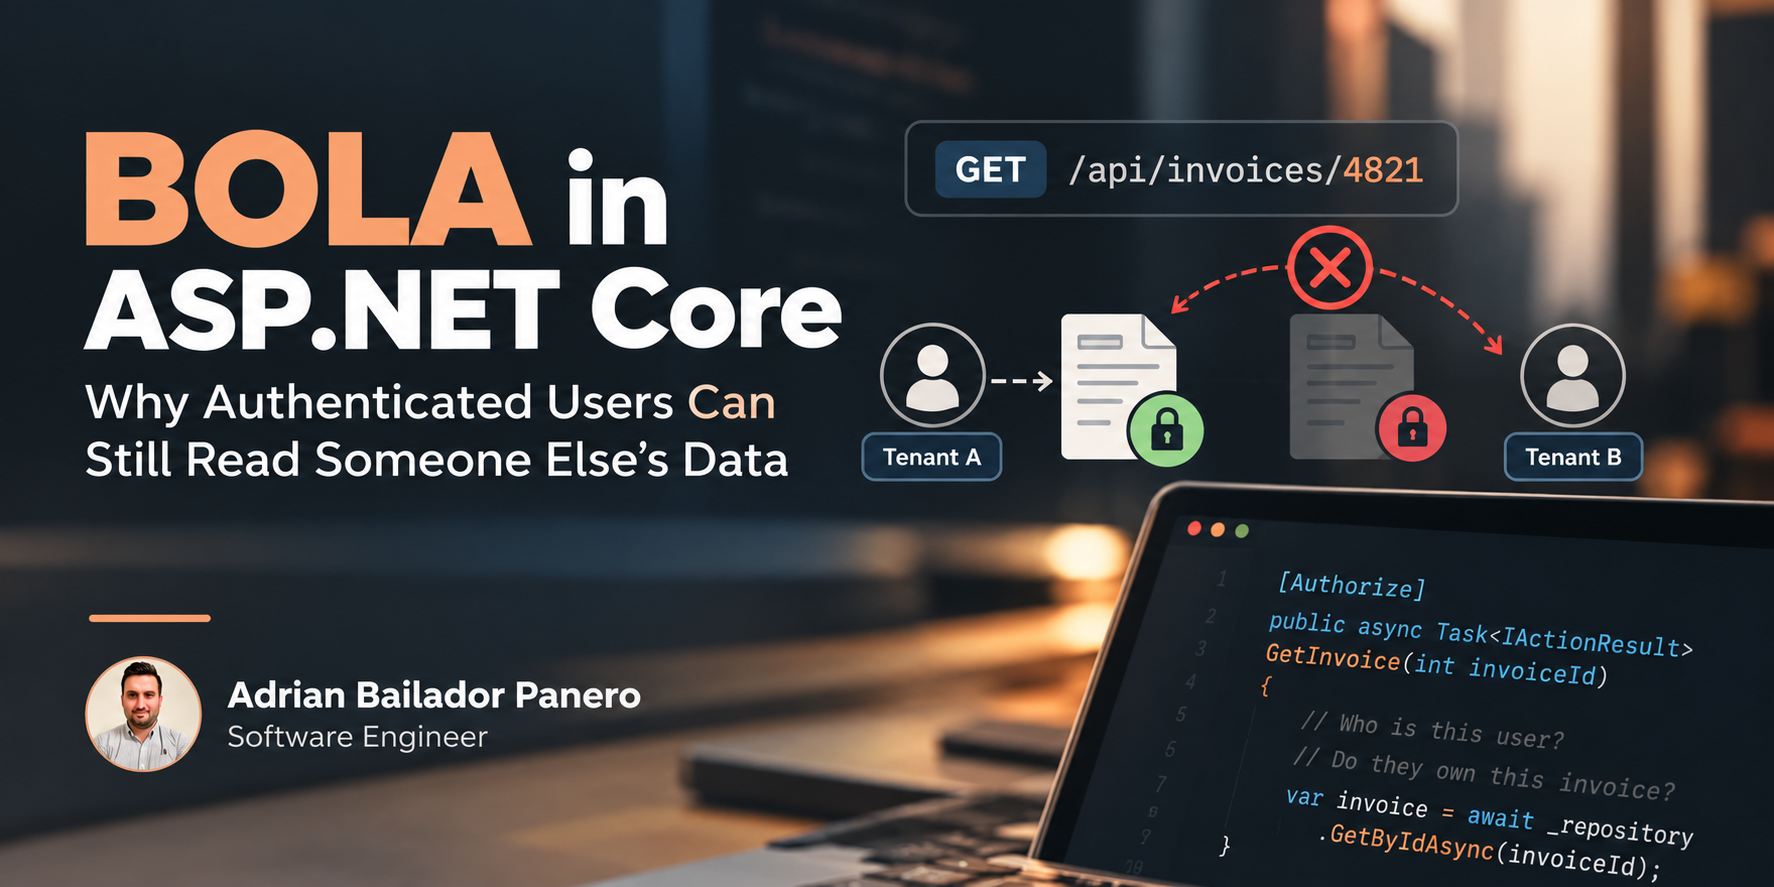
BOLA in ASP.NET Core: Why Authenticated Users Can Still Read Someone Else’s Data
Medium - Adrian Bailador Issue #561
Broken Object Level Authorization is OWASP’s #1 API security risk, and [Authorize] does nothing to stop it.
-

Keep Azure Foundry Hosted Agent credentials out of the browser with a BFF (Backend for Frontend)
C# Corner - Cristopher Coronado Issue #560