security
ASP.NET Core and .NET Security Articles, Tutorials & News
ASP.NET Core and .NET Security articles, tutorials, and news from the DotNetNews archive.
547 articles Updated Page 2 of 22
Browse additional ASP.NET Core and .NET Security articles from the DotNetNews archive.
ASP.NET Core and .NET Security articles
Page 2 of 22
Newest first
-

Use crypto.parsePKCS12() to Read PKCS#12 Files in Node.js
C# Corner - Saurav Kumar Issue #560
-
Azure Key Vault and BYOK: Lessons Learned
Microsoft Tech Community - gurjsing Issue #560
Bring Your Own Key (BYOK) lets you import externally generated key material into Azure Key Vault. Importing that material again creates a new version; it does not recreate the original version identif...
-
What’s Inside That Bearer Token? A Practical Guide to Encrypted JWTs (JWE) in .NET
Medium - Robert Dennyson Issue #559
How to recognize a JWE, inspect its header, and decrypt it safely with .NET when you own the right key.
-
Multi-tenant reporting in ASP.NET Core: row-level security your users can’t bypass
Medium - Dotnet Report Builder Issue #559
By Razi Syed. Sample code for this article: github.com/dotnetreport/dotnetreport-multitenant-rls
-
The 2 AM Bug That Taught Me How Obfuscation Actually Breaks Your Code
Medium - Skater .NET Obfuscator Issue #559
I used to think obfuscation was a “flip the switch and ship it” kind of tool. Then I spent a night debugging a TypeLoadException in a…
-

What Changes When an AI Agent Runs Without a User?
C# Corner - Aarav Patel Issue #557
-
GitHub Copilot Agent Mode: How to Control What an AI Coding Agent Can Do
C# Corner - Aarav Patel Issue #557
-
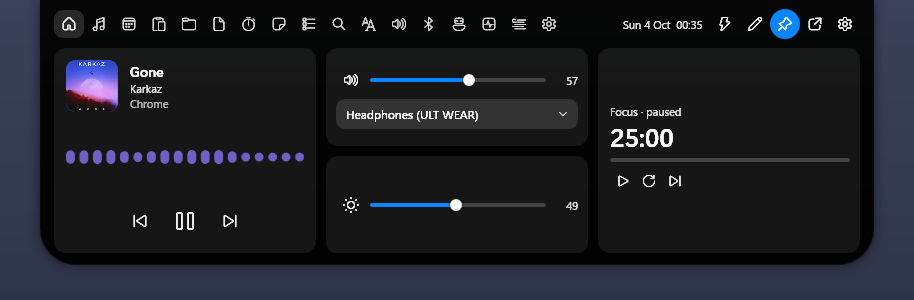
Building NotchX: A Privacy-First “Dynamic Island” for Windows
Medium - Navneetbhogal Issue #556
How I turned a Mac app I loved into a Windows tool - and why I treated a desktop utility like privileged software.
-

GitHub App Tokens Are Getting Longer: What Should Developers Check?
C# Corner - Aarav Patel Issue #555
-
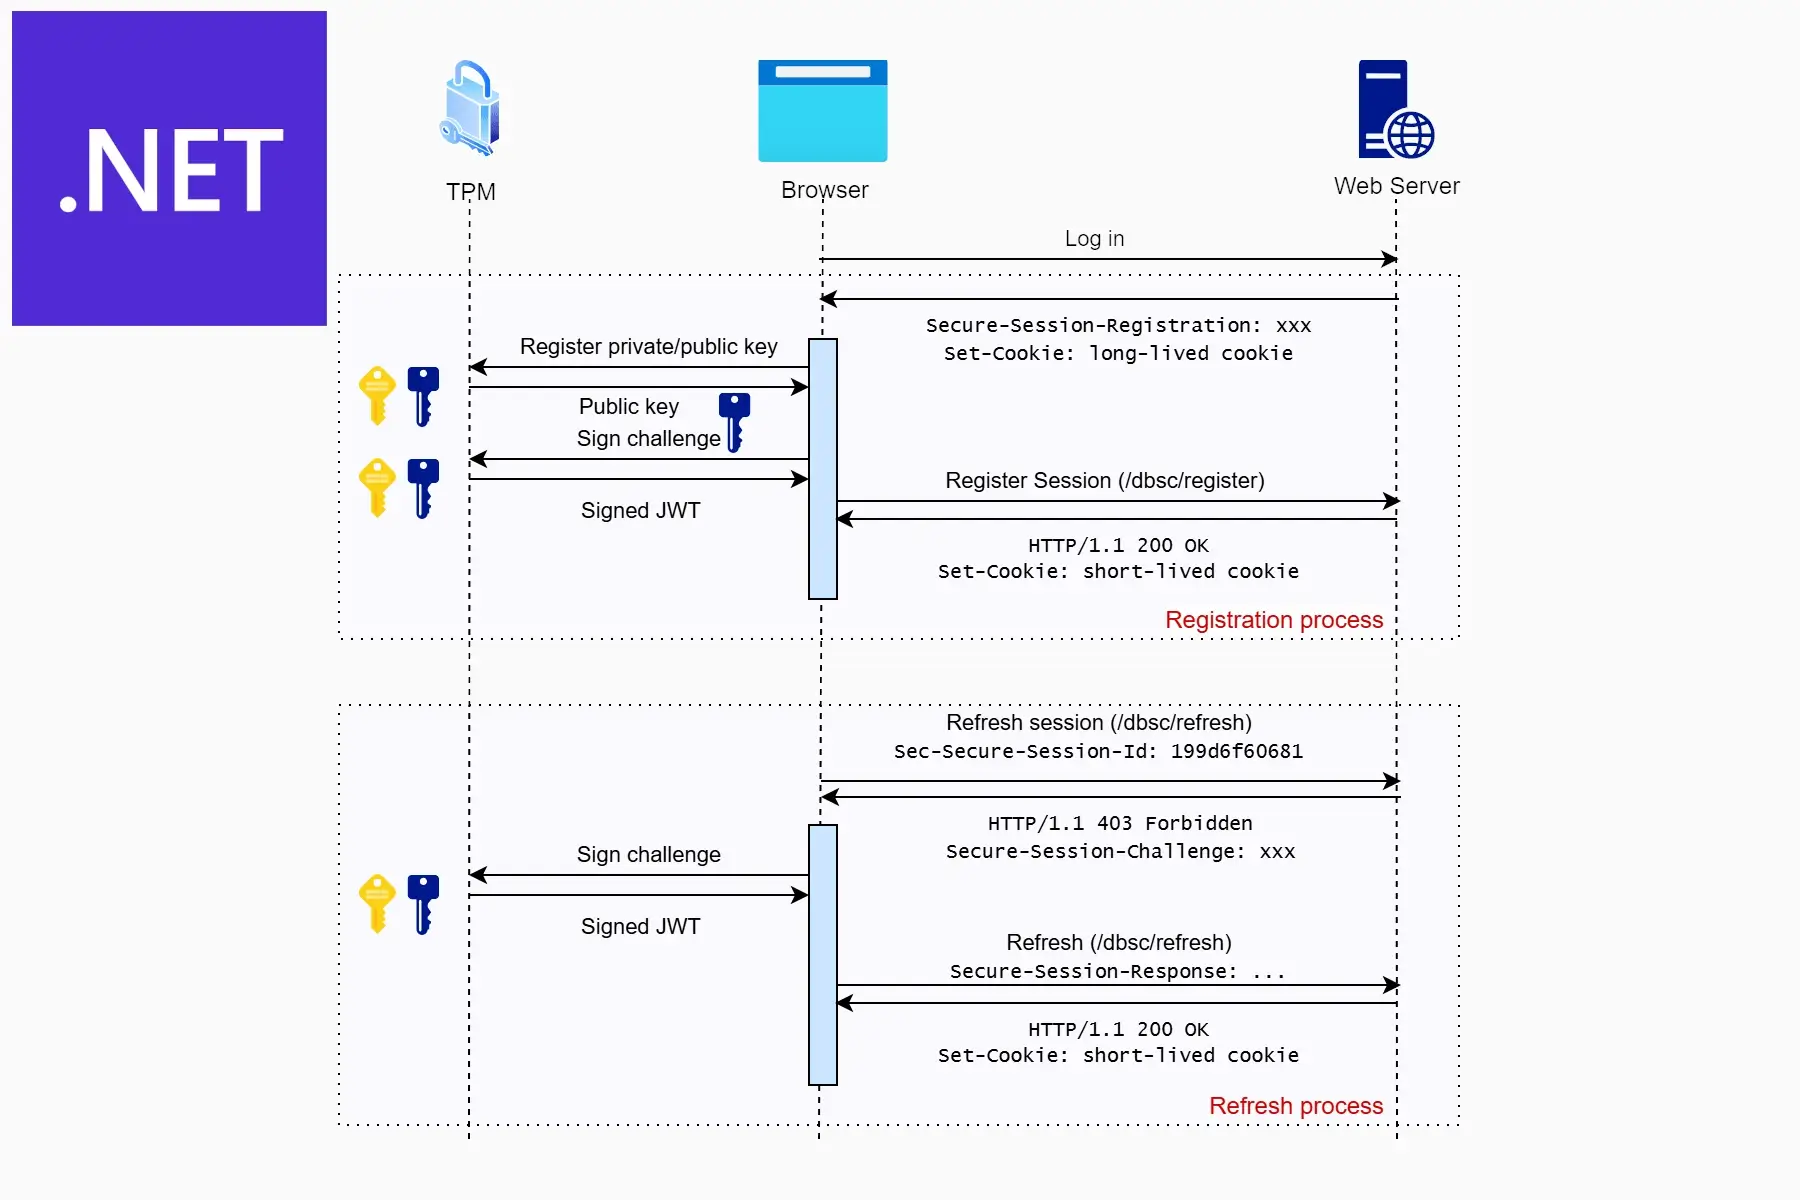
Experimental support for Device Bound Session Credentials (DBSC) in ASP.NET Core: Exploring the .NET 11 preview - Part 8
Andrew Lock | .NET Escapades Issue #554
In this post I look at the new experimental support for DBSC provided by the Microsoft.AspNetCore.Authentication.DeviceBoundSessions package
-
My coding agent wrote outside the repo. Nothing stopped it.
Goat Review - Cyril Canovas Issue #553
You let a coding agent loose on a repository. It reads what it needs, then writes — a file two directories up, a ~/.config it had no business in, a /tmp script it runs next. When you look at how, the ...
-
VS Code Learn: Extending Agents
YouTube - Visual Studio Code Issue #553
Checkout key aspects of AI Agents with Tools, Tool sets, Permissions and Sandboxing. We'll also look at MCP (Model Context Protocol) and how to use it to connect your agents to external data sources. ...
-
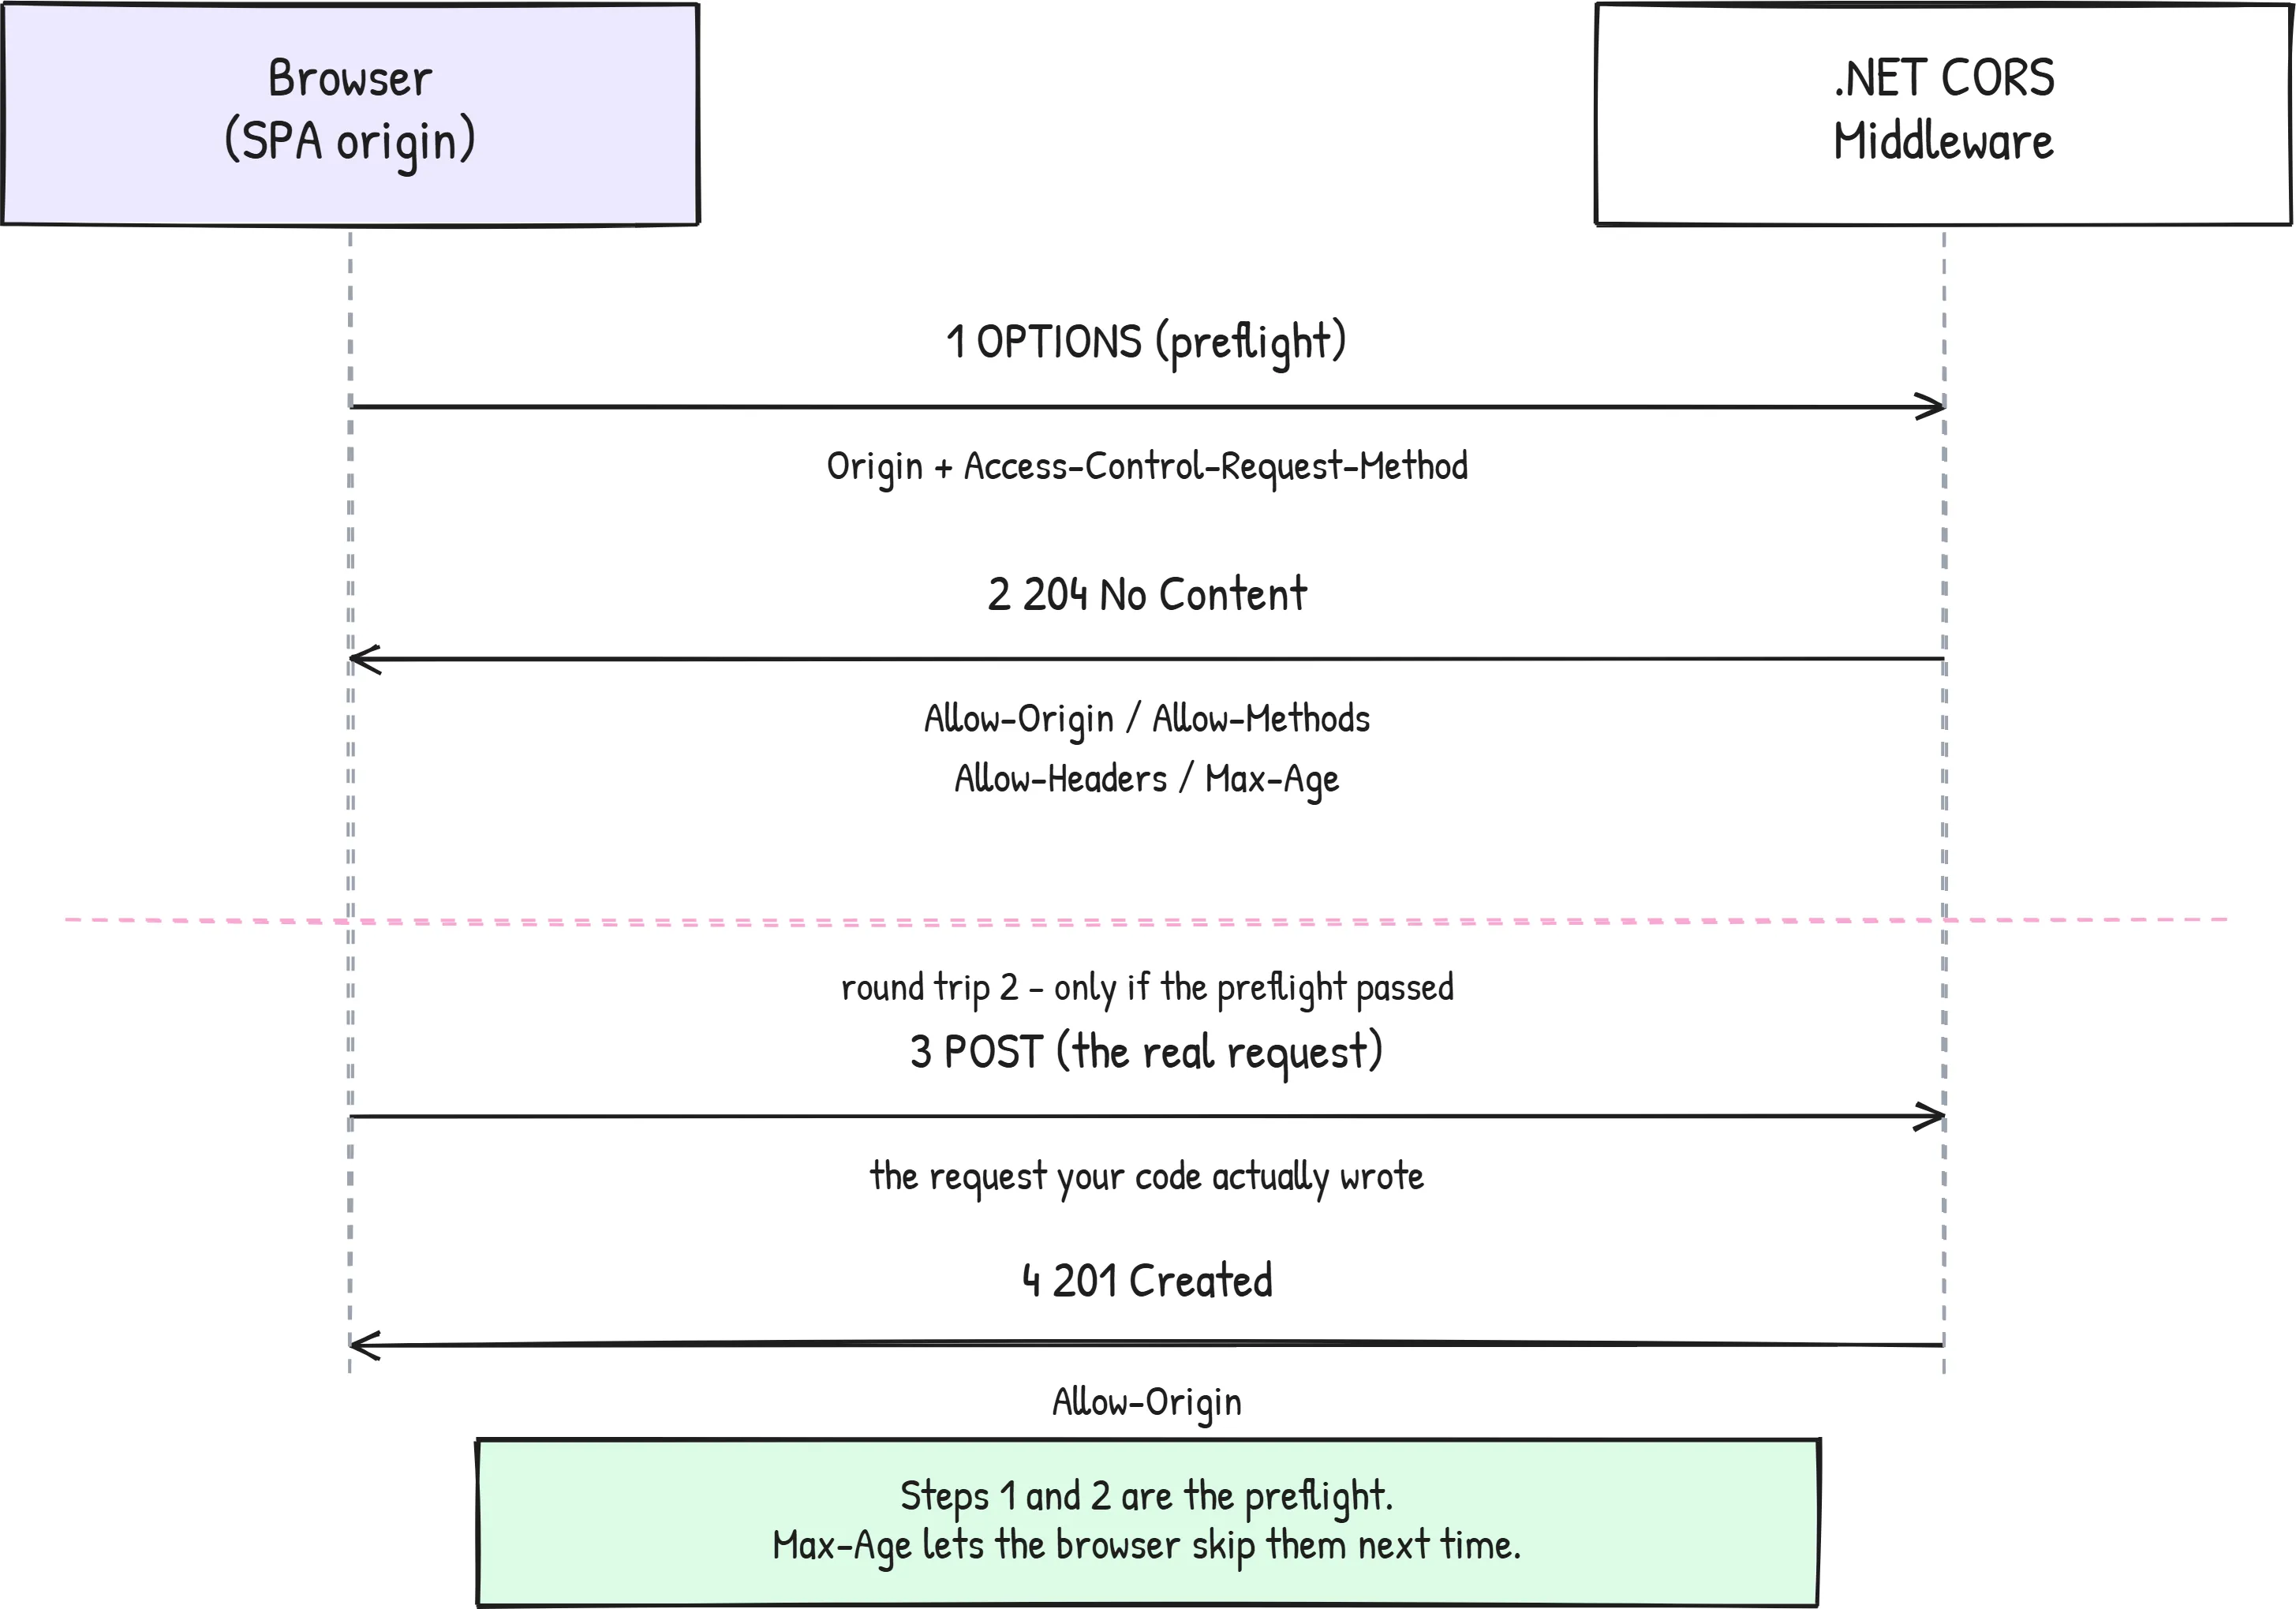
CORS in ASP.NET Core (.NET 10) - Cross-Origin Done Right
codewithmukesh Issue #552
Configure CORS in ASP.NET Core .NET 10. Preflight, named policies, the AllowAnyOrigin + AllowCredentials trap, 7 misconfigurations, and a production checklist.
-
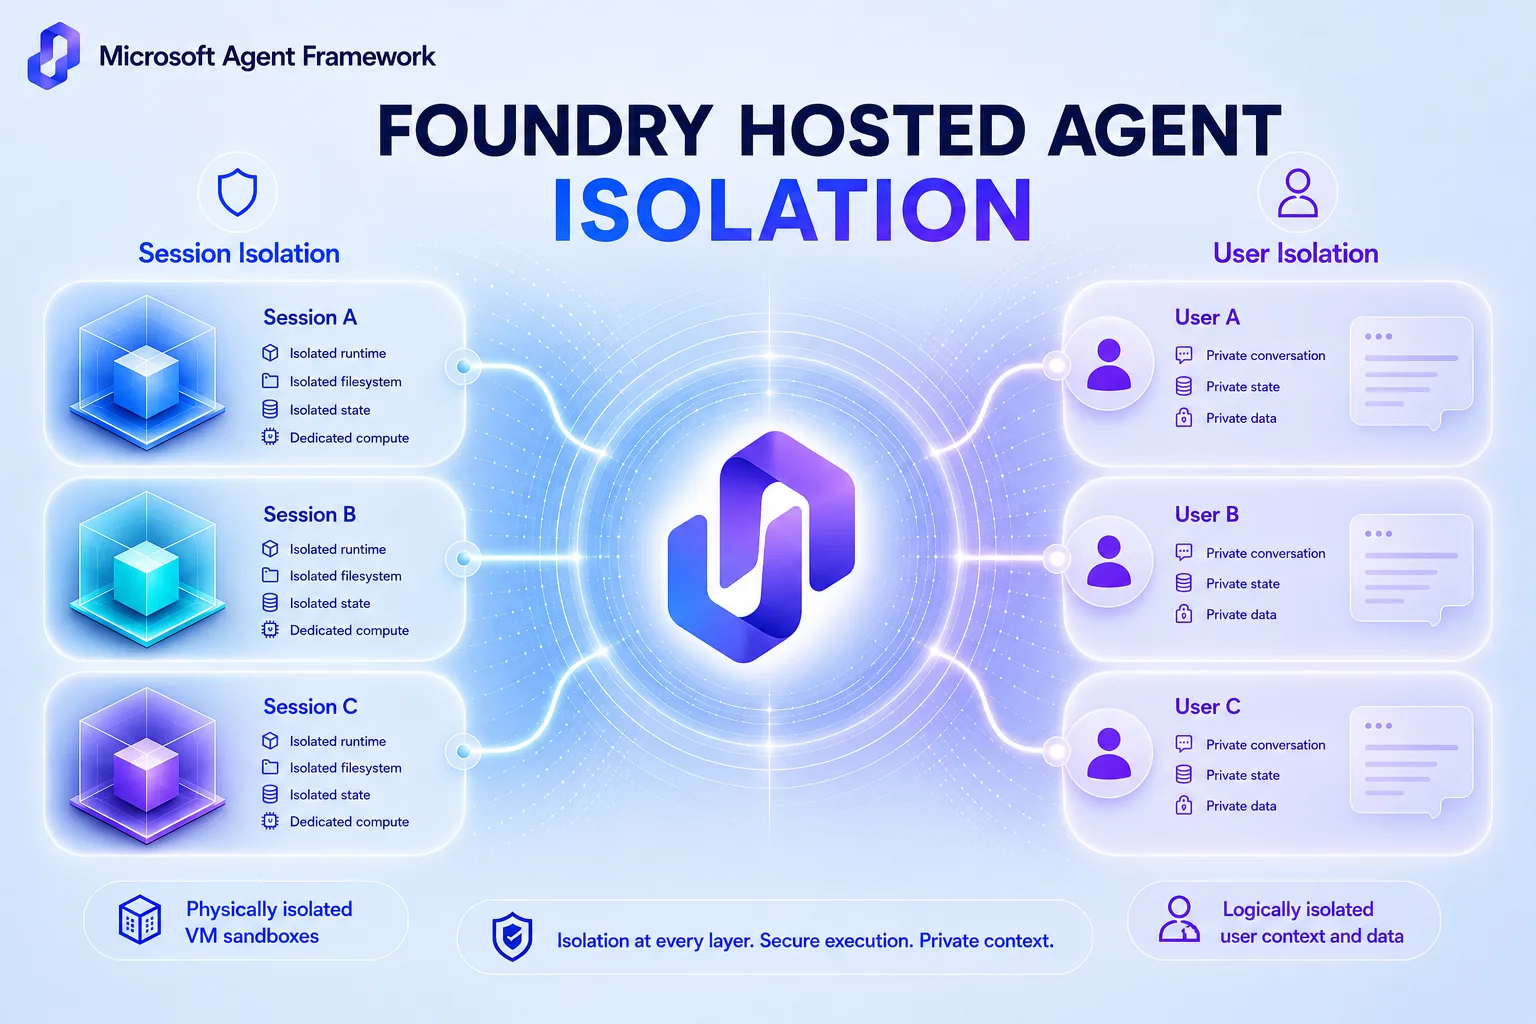
Foundry hosted agent isolation with Microsoft Agent Framework
Microsoft Dev Blogs - Roger Barreto Issue #550
Foundry hosted agent isolation exposes two independent controls. User isolation identifies whose data may be used. At the same time, Foundry hosted session isolation identifies where code and files co...
-
What .NET Code Protection Actually Does (And Why Decompilers Make It Necessary)
Medium Issue #549
.NET code protection exists because of a structural property of the platform: assemblies compile to CIL, an intermediate language that…
-
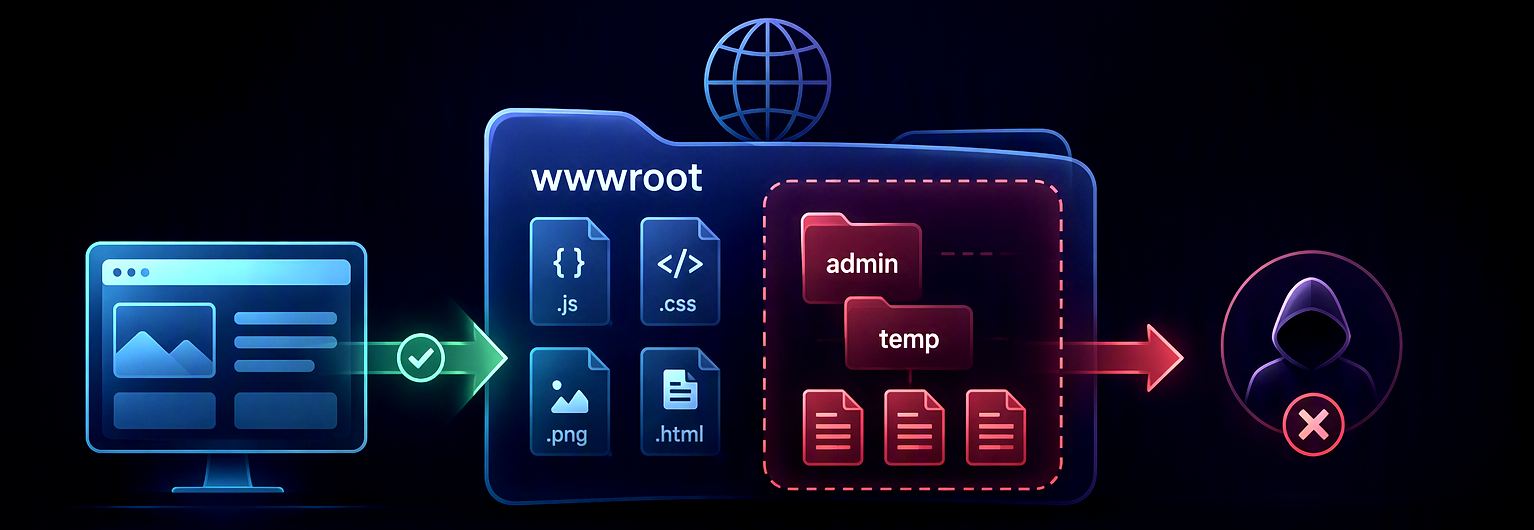
Protecting File Access in the wwwroot Folder in ASP.NET
Rick Strahl's Weblog Issue #547
In many of my applications I have a few files that are dynamically created as part of administrative tasks. These files tend to be cumulative and contain data that can be accessed directly from the fi...
-
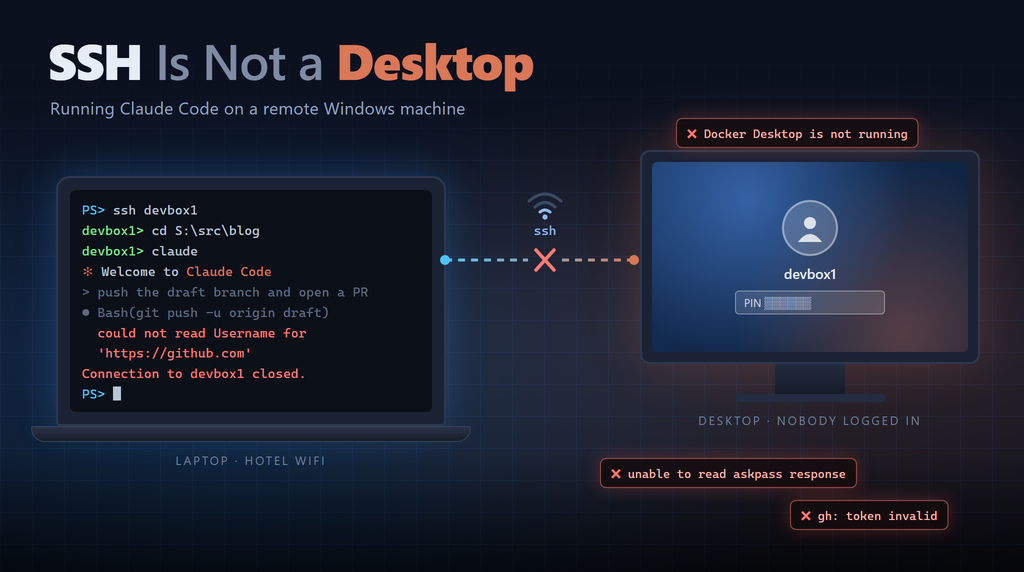
SSH Is Not a Desktop
Rockford Lhotka's Blog Issue #545
I work across three physical PCs. Two of them (I’ll call them devbox1 and devbox2 ) are powerful desktop machines that sit in my office and run all the time. The third is my laptop, which goes with me...
-
PDF Security in .NET: Encryption, Redaction, and Digital Signatures
Medium Issue #545
PDF security is not limited to putting a password on a file.
-
Massive AutoMapper Vulnerability in .NET
YouTube Issue #544
Get every Dometrain 30% off with code HANDSON30: https://dometrain.com/courses/?ref=nick-chapsas&promo=youtube&coupon_code=HANDSON30 Hello, everybody. I'm Nick, and in this video, I will talk about th...
-
Can You Trust an LLM to Fix a Broken Locator?
Medium Issue #542
A measured study of multi-provider LLM consensus as a locator-healing signal — and why Automation Sandbox keeps the LLM out of the…
-
GitHub Copilot Agent Plugins: Testing Plugin Trust Across VS Code and Copilot CLI
C# Corner Issue #542
Learn how to test GitHub Copilot agent plugins across VS Code and Copilot CLI, focusing on trust, permissions, reproducibility, tool access, and security controls.
-
Let Postgres Enforce Tenant Isolation
Milan's .NET Weekly Issue #542
EF Core query filters can be bypassed. PostgreSQL row-level security enforces tenant isolation on reads and writes, if you connect with the right database role…
-
GitHub Copilot Agent Plugins: Testing Plugin Trust Across VS Code and Copilot CLI
C# Corner Issue #541
Learn how to test GitHub Copilot agent plugin trust across VS Code and Copilot CLI, including permissions, tool access, security, and reproducibility.
-
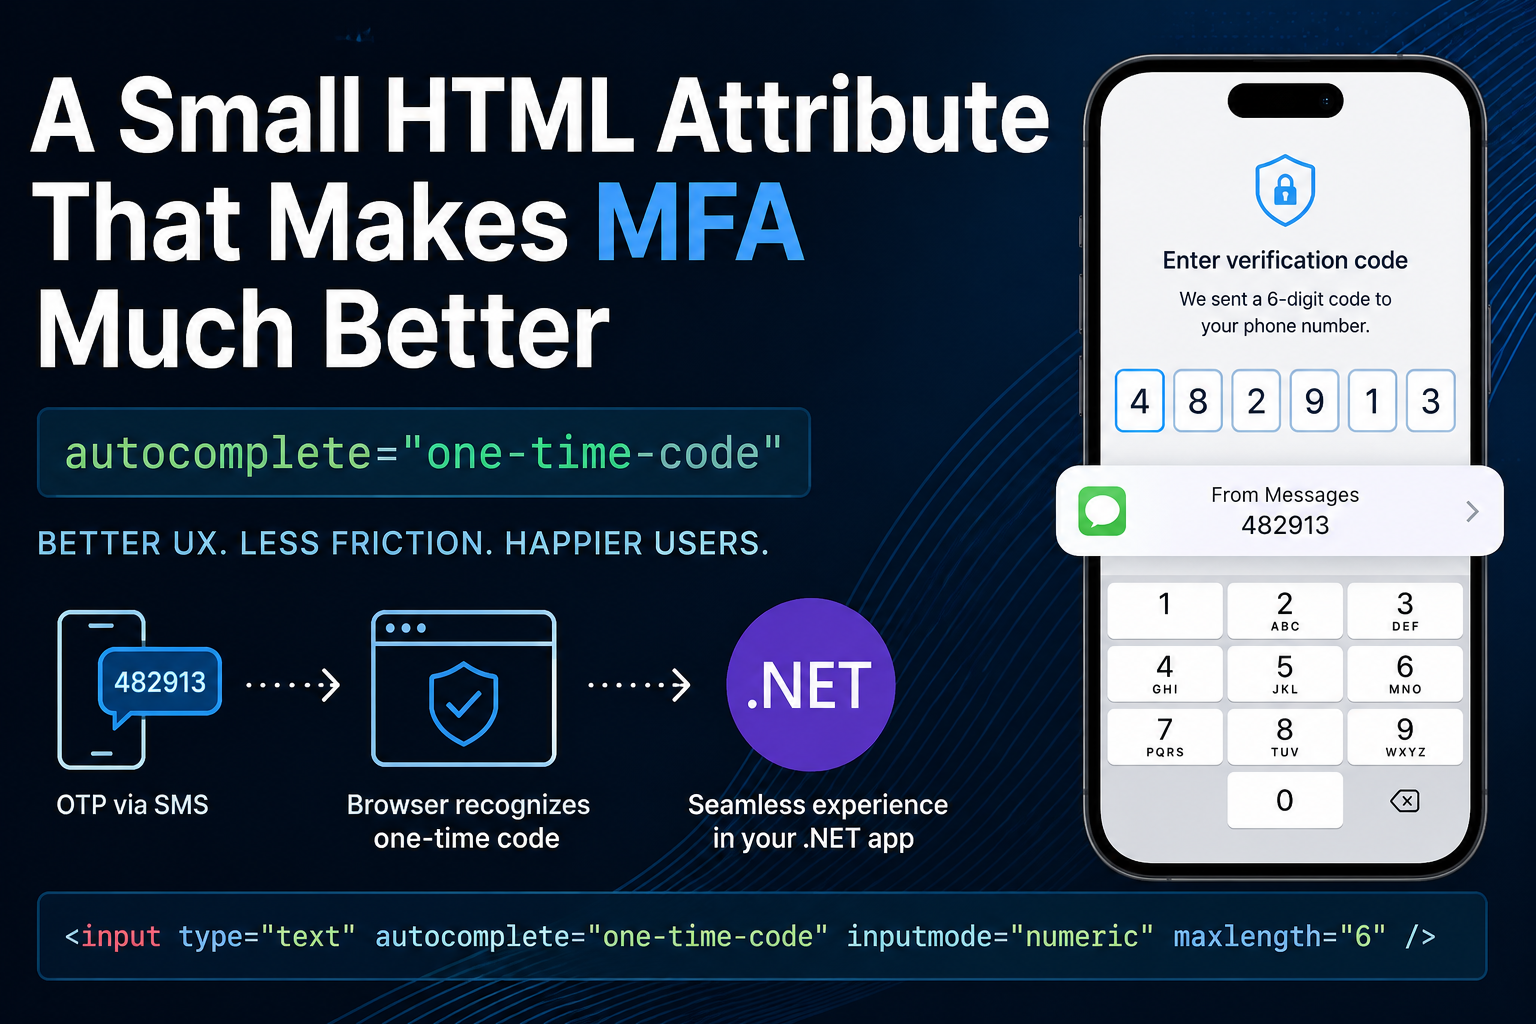
A Small HTML Attribute That Makes MFA Much Better
Medium Issue #538
Discover how one HTML attribute can make MFA faster, simpler, and more user-friendly in your .NET applications.
-
How Can Enterprises Secure ASP.NET Core APIs in Production?
Medium Issue #537
APIs have become the connective tissue of modern enterprise applications. They connect web and mobile applications, cloud services…