security
ASP.NET Core and .NET Security Articles, Tutorials & News
ASP.NET Core and .NET Security articles, tutorials, and news from the DotNetNews archive.
520 articles Updated Page 4 of 21
Browse additional ASP.NET Core and .NET Security articles from the DotNetNews archive.
ASP.NET Core and .NET Security articles
Page 4 of 21
Newest first
-
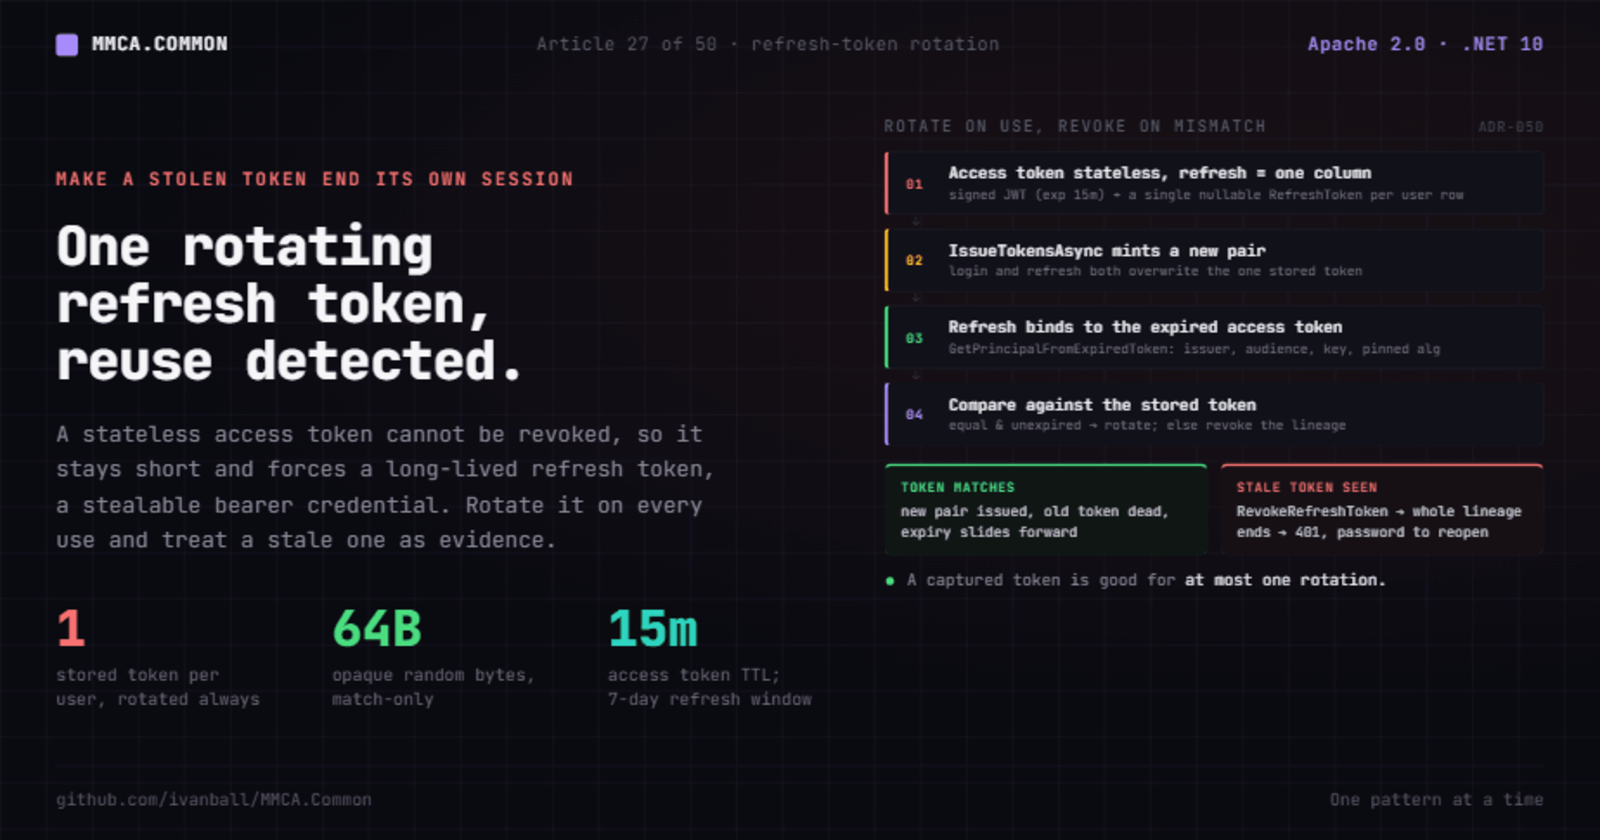
One rotating refresh token, and reuse detection that makes theft self-limiting
Medium Issue #513
A stateless JWT you cannot revoke has to be short-lived, which forces a refresh token, which is a long-lived bearer credential that can be…
-

Secure File Uploads in ASP.NET Core: Validation, Storage, and Best Practices
C# Corner Issue #513
Master secure file uploads in ASP.NET Core. Learn validation, storage, and best practices to prevent security risks and ensure robust applications.
-

Secure Secrets Management in ASP.NET Core: User Secrets, Azure Key Vault, and Production Best Practices
C# Corner Issue #512
Secure ASP.NET Core secrets with User Secrets, Azure Key Vault, and best practices. Protect your app from development to production.
-
Device Code Flow: The Gift That Keeps on Giving — To Attackers
Microsoft Tech Community Issue #512
PENDING REVIEW: MICROSOFT ARTICLE UNRETRIEVABLE (HTTP 403). Tags: Microsoft Entra ID, Conditional Access, Device Code Flow, OAuth, Azure Arc, Azure Migrate, Identity Security, Zero Trust Introduction ...
-
Building Secure File Upload APIs in ASP.NET Core 10
C# Corner Issue #512
Build secure ASP.NET Core file upload APIs. Learn validation, size limits, safe storage, and best practices to prevent vulnerabilities.
-
API Gateway Patterns in ASP.NET Core with YARP: Routing, Security, and Load Balancing
C# Corner Issue #512
Build production-ready API Gateways in ASP.NET Core with YARP for routing, security, load balancing, and scalable microservices.
-
Prioritize exposure resolution with a new dashboard experience (public preview)
Microsoft Tech Community Issue #512
PENDING REVIEW: MICROSOFT ARTICLE UNRETRIEVABLE (HTTP 403). Cut Through the Noise and Focus on What Matters Most Security teams face a constant challenge: too many findings, too many dashboards, and n...
-
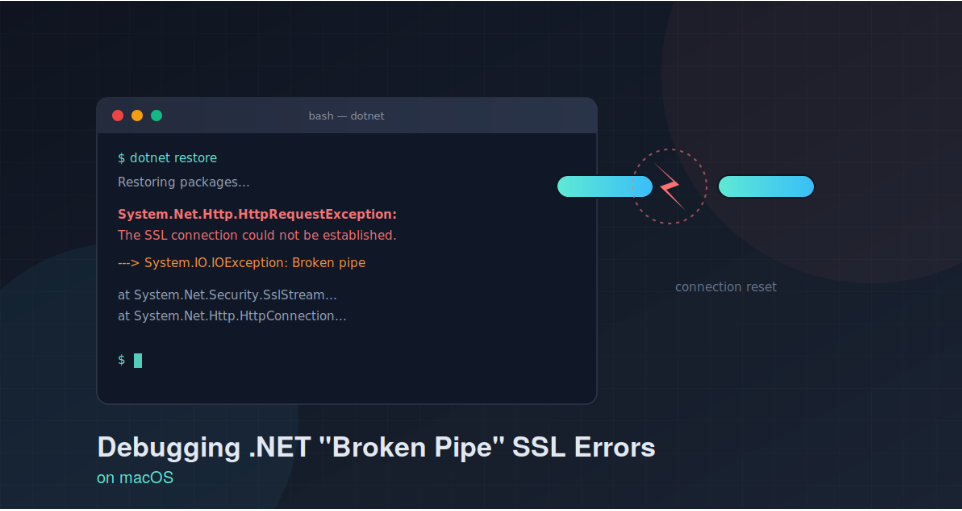
Debugging .NET “Broken Pipe” SSL Errors on macOS
Medium Issue #512
One of the more frustrating .NET errors on macOS is:
-

AI Governance and Autonomous AI Agent Governance: From Controlling Models to Governing Digital Actors - Human-in-the-Loop Is Not Enough
C# Corner Issue #512
AI governance evolves from model control to governing autonomous digital actors, emphasizing identity, authorization, and accountability for responsible operations.
-
How Nationwide stays ahead of attackers with Project Perception
Microsoft Tech Community Issue #512
PENDING REVIEW: MICROSOFT ARTICLE UNRETRIEVABLE (HTTP 403). Nationwide, the world’s largest building society, is among the first organizations to put Microsoft’s new...
-

Rate Limiting in ASP.NET Core: Protecting APIs from Abuse and Traffic Spikes
C# Corner Issue #511
Protect ASP.NET Core APIs from abuse & traffic spikes with built-in rate limiting. Implement policies for robust security & performance.
-
Secure Secrets Management in ASP.NET Core: User Secrets, Azure Key Vault, and Environment Variables
C# Corner Issue #510
Secure your ASP.NET Core apps! Learn User Secrets, Azure Key Vault, & Env Vars for robust secrets management. Avoid breaches.
-
Understanding the Fetch Metadata HTTP headers: Sec-Fetch-Site and friends
Andrew Lock | .NET Escapades Issue #510
In this post I describe the Fetch Metadata HTTP headers like Sec-Fetch-Site and Sec-Fetch-Mode which give information to a server about the context of a request
-
MCP Security Best Practices: Authentication, Authorization, and Secure Tooling
C# Corner Issue #509
Secure your .NET MCP implementations with best practices for authentication, authorization, and tool design to protect AI integrations and enterprise data.
-
Securing ASP.NET Core APIs with Microsoft Entra ID Authentication
C# Corner Issue #508
Secure ASP.NET Core APIs with Microsoft Entra ID. Learn authentication, configuration, and best practices for robust API security.
-

GitHub Copilot Enterprise Best Practices for .NET Teams
C# Corner Issue #508
Unlock GitHub Copilot Enterprise for .NET teams! Master best practices for AI-assisted coding, ensuring quality, security, and maintainability.
-
Rate Limiting in ASP.NET Core APIs: Best Practices for Scalable and Secure Applications
C# Corner Issue #507
Master ASP.NET Core rate limiting for scalable, secure APIs. Learn best practices, algorithms (fixed, sliding, token bucket), and middleware for robust traffic control.
-
Secure Secrets Management in .NET with Azure Key Vault
C# Corner Issue #507
Secure your .NET apps with Azure Key Vault. Learn to manage secrets, keys, and certs centrally, avoiding hardcoding and enhancing security.
-

Secure AI Applications in ASP.NET Core: Preventing Prompt Injection and Data Leakage
C# Corner Issue #506
Secure ASP.NET Core AI apps against prompt injection & data leakage. Learn best practices for LLM security, RAG, and tool access.
-
Migrate Legacy ASP.NET Apps to .NET 10
C# Corner Issue #506
Migrate legacy ASP.NET apps to .NET 10 for improved performance, security, and modern features. Learn the process and best practices.
-
Implementing Rate Limiting in ASP.NET Core for Secure and Scalable APIs
C# Corner Issue #506
Secure your ASP.NET Core APIs with rate limiting. Learn to implement fixed window, sliding window, and token bucket strategies for robust protection.
-
Building Secure REST APIs with ASP.NET Core and API Versioning Best Practices
C# Corner Issue #505
Build secure, versioned REST APIs in ASP.NET Core. Learn JWT auth, HTTPS, validation, and versioning best practices for reliable apps.
-

Password hashing done right: PBKDF2-SHA512, 600k iterations, timing-safe
Medium Issue #504
Storing a password is a solved problem, and almost every breach headline is someone who solved it the wrong way. Here are the four…
-

Cross-service auth without a shared secret: JWKS dual-fetch
Medium Issue #502
When you split a monolith into services, the easy answer is to copy the JWT signing secret into every validator. That is also the answer…
-

Implementing Passkey Authentication in ASP.NET Core Applications
C# Corner Issue #502
Implement secure, passwordless passkey authentication in ASP.NET Core. Leverage FIDO2 & WebAuthn for enhanced security and user experience.