security
JWT Authentication in ASP.NET Core Articles, Tutorials & News
JWT Authentication in ASP.NET Core articles, tutorials, and news from the DotNetNews archive.
87 articles Updated
JWT Authentication in ASP.NET Core work shows up across many DotNetNews issues because teams keep hitting the same implementation questions. JWT Authentication in ASP.NET Core sits in the ASP.NET Core and broader Microsoft web stack that most C# services use.
Recurring subtopics in recent issues include JWT authentication ASP.NET Core, JWT C#, Bearer tokens ASP.NET Core, and JSON Web Token .NET. When a subtopic never appears in the archive titles or excerpts, it is left out of this introduction.
Expect publisher tutorials, release notes, architecture write-ups, and field notes linked from DotNetNews issues. Start here is a short editorial shortlist for JWT Authentication in ASP.NET Core; the archive list is chronological and larger. Secondary angles such as JWT authentication ASP.NET Core and JWT C# appear when the archive actually covered them. Cross-links to ASP.NET Core Authentication and ASP.NET Core Authorization help when the problem spans more than one tag.
Each card points at the original publisher URL and the DotNetNews issue that carried it, so you can read the article in context or jump straight to the source.
Start here
Editor picks for JWT
-

Cross-service auth without a shared secret: JWKS dual-fetch
Medium Issue #502
Good architecture-level auth guidance. Avoiding shared signing secrets across services is the right problem to solve.
-

Why Modern ASP.NET Core Web APIs Use JWT Instead of Sessions
Medium Issue #500
A straightforward API security primer that explains why stateless tokens fit modern multi-client apps better than server sessions.
-

Secure AI APIs in ASP.NET Core with Token-Based Authorization and Rate Limiting
C# Corner Issue #500
Timely combination of authz and rate limiting for AI endpoints, where abuse prevention is now part of basic API design.
-

Validating and Authorizing JWTs in a Serverless Multi-Agent RAG Backend
C# Corner Issue #496
Secure serverless RAG with JWT validation & authorization.
-
JWT Done Right: 15 Production Mistakes Every ASP.NET Core Developer Should Avoid (.NET 9 Guide)
Medium Issue #492
JWT advice is often too shallow; this one aims at the production mistakes that actually cause incidents.
-
Role-Based Authorization in ASP.NET Core - A .NET 10 Guide
codewithmukesh Issue #481
Implement role-based authorization in ASP.NET Core .NET 10, add roles to JWTs, protect Minimal API endpoints with RequireRole, and fix roles that won't map.
-

JWT Authentication in ASP.NET Core - A Complete .NET 10 Guide
codewithmukesh Issue #471
Complete JWT implementation guide covering token generation, validation, and role-based authorization in .NET 10.
-
How to Add JWT Authentication to SignalR Hubs in ASP.NET Core
Dev Tips Issue #428
An interesting AI integration guide for teams experimenting with Claude inside ASP.NET Core instead of around it.
Archive
Page 1 of 4
Newest first
-
What’s Inside That Bearer Token? A Practical Guide to Encrypted JWTs (JWE) in .NET
Medium - Robert Dennyson Issue #559
How to recognize a JWE, inspect its header, and decrypt it safely with .NET when you own the right key.
-
How to Add JWT Authentication to SignalR Hubs in ASP.NET Core
Medium - Anton Martyniuk Issue #552
SignalR makes real-time communication in .NET applications simple. Continue reading on CodeX »
-
7 Authentication Concepts Every Developer Should Know: From Basic Auth to OAuth2 and OIDC
C# Corner Issue #544
A beginner-friendly, diagram-backed walkthrough of the seven core authentication concepts every developer should understand from Basic Auth and sessions to JWTs, OAuth2, and OpenID Connect/SSO with re...
-
ASP.NET Core: JWT Authentication and Authorization
towardsdev.com Issue #528
-
Implementing JWT Authentication with Secure Refresh Tokens in .NET Core
C# Corner Issue #519
Implement secure JWT authentication with refresh tokens in .NET Core. Learn to generate, validate, and refresh tokens for stateless API security.
-
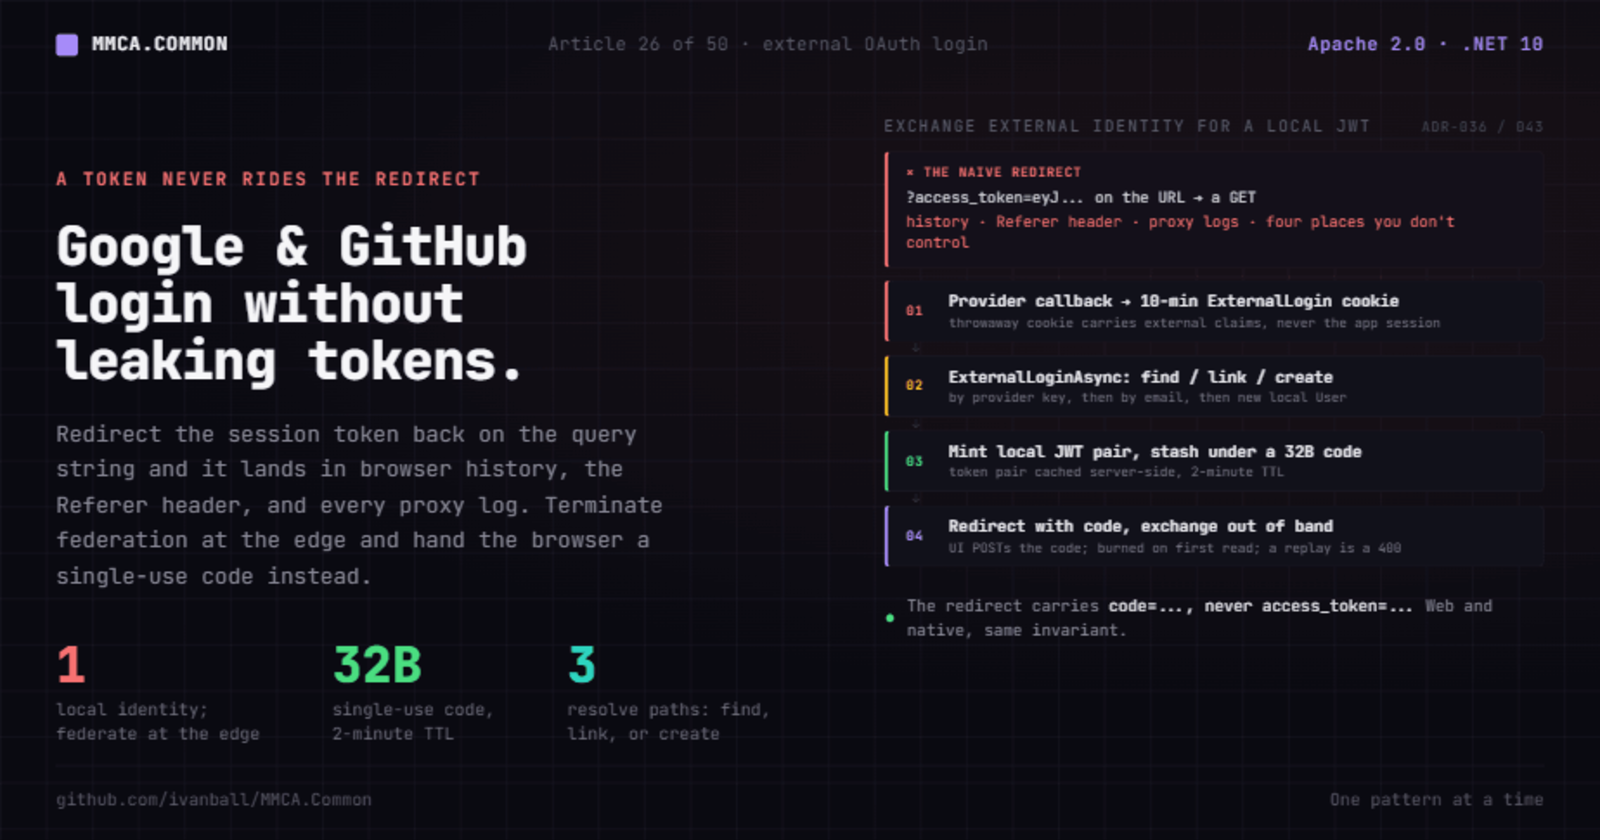
Google and GitHub login without leaking tokens: external OAuth behind your own JWTs
Medium Issue #518
You want “Sign in with Google” and “Sign in with GitHub.”
-
JWT Session 15: Implement Logout and Refresh Token Revocation in ASP.NET Core Web API
C# Corner Issue #518
Secure your JWT-based ASP.NET Core API by implementing robust logout and refresh token revocation to prevent session hijacking and unauthorized access.
-

Integrating Snowflake Cortex AI with Enterprise .NET Applications
C# Corner Issue #517
Integrate Snowflake Cortex AI with .NET apps for secure, in-perimeter LLM inference. Leverage JWTs & native RBAC for data governance.
-

JWT Session 14: Implement Refresh Token Authentication in ASP.NET Core Web API
C# Corner Issue #515
Enhance ASP.NET Core Web API security with JWT refresh tokens. Learn to implement long-lived refresh tokens for seamless user authentication and improved UX.
-

Authentication in ASP.NET Core: JWT vs Cookies vs OAuth 2.0 Explained
C# Corner Issue #514
Master ASP.NET Core authentication: JWT vs Cookies vs OAuth 2.0. Choose the right strategy for security, scalability, and user experience.
-
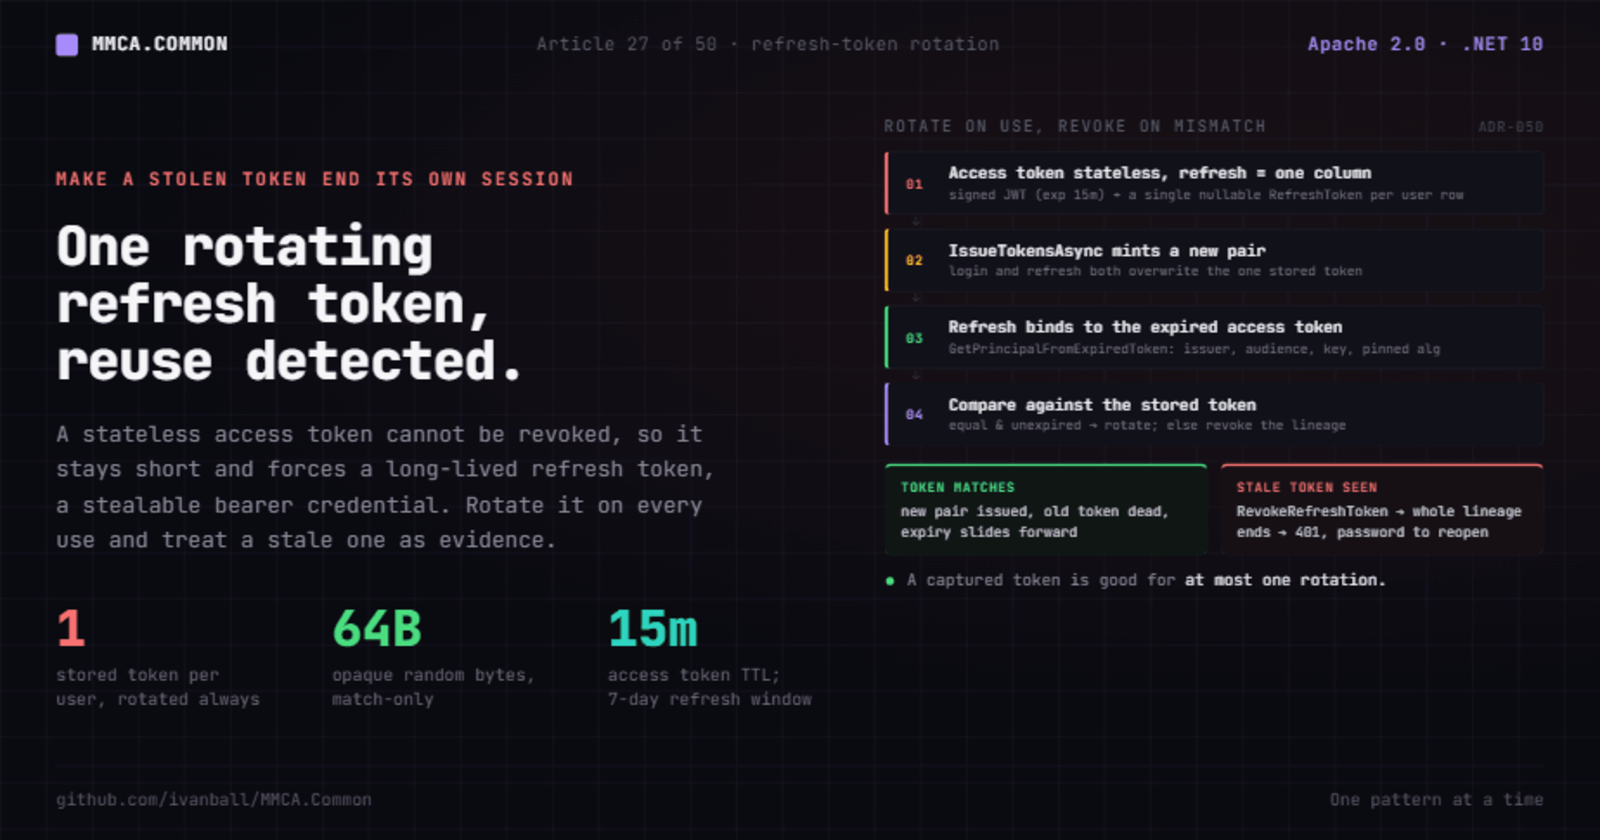
One rotating refresh token, and reuse detection that makes theft self-limiting
Medium Issue #513
A stateless JWT you cannot revoke has to be short-lived, which forces a refresh token, which is a long-lived bearer credential that can be…
-
OAuth 2.1 Authentication in ASP.NET Core APIs: A Practical Guide
C# Corner Issue #507
Master OAuth 2.1 for ASP.NET Core APIs. Learn PKCE, JWT validation, refresh tokens, and best practices for secure API authentication.
-
Building Secure REST APIs with ASP.NET Core and API Versioning Best Practices
C# Corner Issue #505
Build secure, versioned REST APIs in ASP.NET Core. Learn JWT auth, HTTPS, validation, and versioning best practices for reliable apps.
-
Cross-service auth without a shared secret: JWKS dual-fetch
Medium Issue #502
When you split a monolith into services, the easy answer is to copy the JWT signing secret into every validator. That is also the answer…
-
Why Modern ASP.NET Core Web APIs Use JWT Instead of Sessions
Medium Issue #500
Modern applications are no longer limited to a single website. A business may have an Angular application, a mobile app, an admin…
-
Secure AI APIs in ASP.NET Core with Token-Based Authorization and Rate Limiting
C# Corner Issue #500
Secure ASP.NET Core AI APIs with JWT, authorization policies, and rate limiting. Protect against abuse and manage costs effectively.
-

How to Secure APIs with OAuth 2.1 and OpenID Connect
C# Corner Issue #498
Secure your APIs with OAuth 2.1 and OpenID Connect. Learn about authentication, authorization, JWTs, PKCE, and best practices for modern applications.
-
Validating and Authorizing JWTs in a Serverless Multi-Agent RAG Backend
C# Corner Issue #496
Secure serverless RAG with JWT validation & authorization. Integrate claims into LangGraph for multi-agent data isolation and compliance.
-
JWT Done Right: 15 Production Mistakes Every ASP.NET Core Developer Should Avoid (.NET 9 Guide)
Medium Issue #492
Fifteen JWT mistakes in ASP.NET Core APIs: validation, refresh tokens, key rotation, revocation, and the controls that must sit beside a…
-
ASP.NET Core Identity with JWT Authentication - Step-by-Step Practical Guide
C# Corner Issue #485
Master ASP.NET Core Identity & JWT for secure user registration, login, and role-based API authorization. A practical step-by-step guide.
-
Role-Based Authorization in ASP.NET Core - A .NET 10 Guide
codewithmukesh Issue #481
Implement role-based authorization in ASP.NET Core .NET 10 - add roles to JWTs, protect Minimal API endpoints with RequireRole, and fix roles that won't map.
-

Securing .net 9 Application Using JWt Refresh Token signup , login
C# Corner Issue #475
Secure .NET 9 apps with JWT refresh tokens. Implement secure signup, login, and resource protection using best practices.
-
JWT Authentication in ASP.NET Core - A Complete .NET 10 Guide
codewithmukesh Issue #471
Implement JWT authentication in ASP.NET Core .NET 10 - generate signed tokens with JsonWebTokenHandler, secure Minimal API endpoints, and add role-based authorization.
-
RestSharp in Practice (Part 2) POST, PUT, DELETE, and JWT Authentication
Medium Issue #471
RestSharp in Practice (Part 2)
-

Refresh Tokens in ASP.NET Core - A Complete .NET 10 Guide
codewithmukesh Issue #471
Implement refresh tokens in ASP.NET Core .NET 10 - token rotation, reuse detection, revocation, and where to store them, built on top of JWT authentication.