security
ASP.NET Core Authentication Articles, Tutorials & News
ASP.NET Core Authentication articles, tutorials, and news from the DotNetNews archive.
196 articles Updated Page 2 of 8
Browse additional ASP.NET Core Authentication articles from the DotNetNews archive.
ASP.NET Core Authentication articles
Page 2 of 8
Newest first
-
Modern authentication in ASP.NET Core with 2FA and passkey
elmah.io Blog - .NET Technical tutorials/guides and new features Issue #519
This walkthrough builds a .NET 10 ASP.NET Core Web API (TwoFaNET10) implementing two-factor authentication and WebAuthn/FIDO2 passkey login, using Microsoft.AspNetCore.Identity.EntityFrameworkCore wit...
-

Implementing JWT Authentication with Secure Refresh Tokens in .NET Core
C# Corner Issue #519
Implement secure JWT authentication with refresh tokens in .NET Core. Learn to generate, validate, and refresh tokens for stateless API security.
-
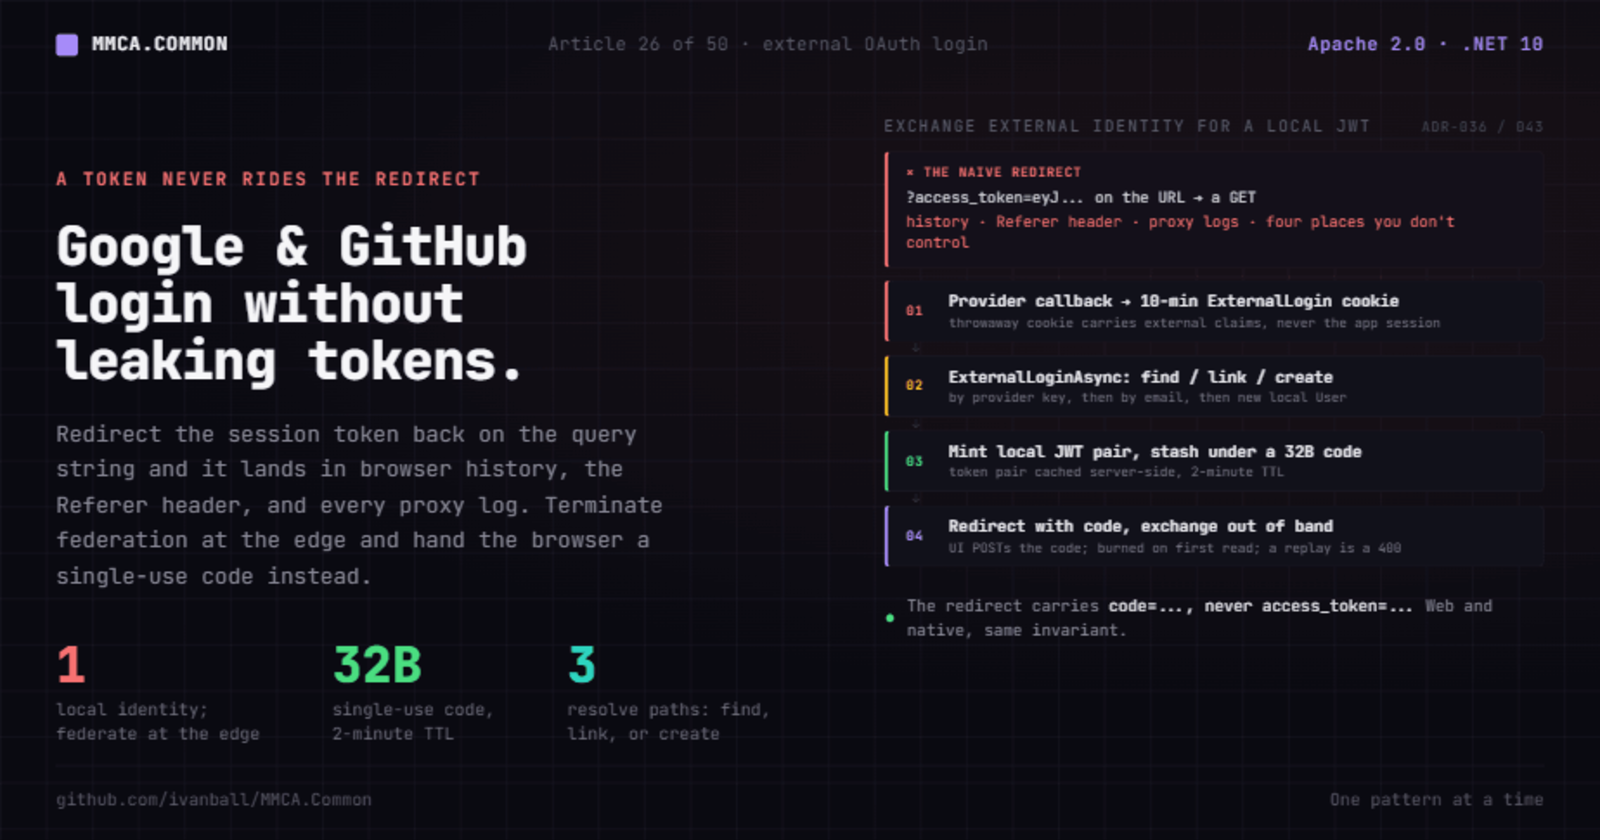
Google and GitHub login without leaking tokens: external OAuth behind your own JWTs
Medium Issue #518
You want “Sign in with Google” and “Sign in with GitHub.”
-
ASP.NET Core 10 Authentication & Authorization Best Practices
C# Corner Issue #517
Master ASP.NET Core 10 authentication & authorization best practices. Secure your APIs, protect user data, and build production-ready applications.
-

JWT Session 14: Implement Refresh Token Authentication in ASP.NET Core Web API
C# Corner Issue #515
Enhance ASP.NET Core Web API security with JWT refresh tokens. Learn to implement long-lived refresh tokens for seamless user authentication and improved UX.
-

Understanding the Role of Microsoft Entra ID in Microsoft Intune
C# Corner Issue #515
Discover how Microsoft Entra ID powers Intune for secure device management, user authentication, and policy enforcement for your organization.
-
Implementing Passkeys in ASP.NET Core Identity Without Breaking Existing Authentication
C# Corner Issue #514
Implement passkeys in ASP.NET Core Identity without breaking existing authentication. Enable passwordless login gradually.
-

Authentication in ASP.NET Core: JWT vs Cookies vs OAuth 2.0 Explained
C# Corner Issue #514
Master ASP.NET Core authentication: JWT vs Cookies vs OAuth 2.0. Choose the right strategy for security, scalability, and user experience.
-
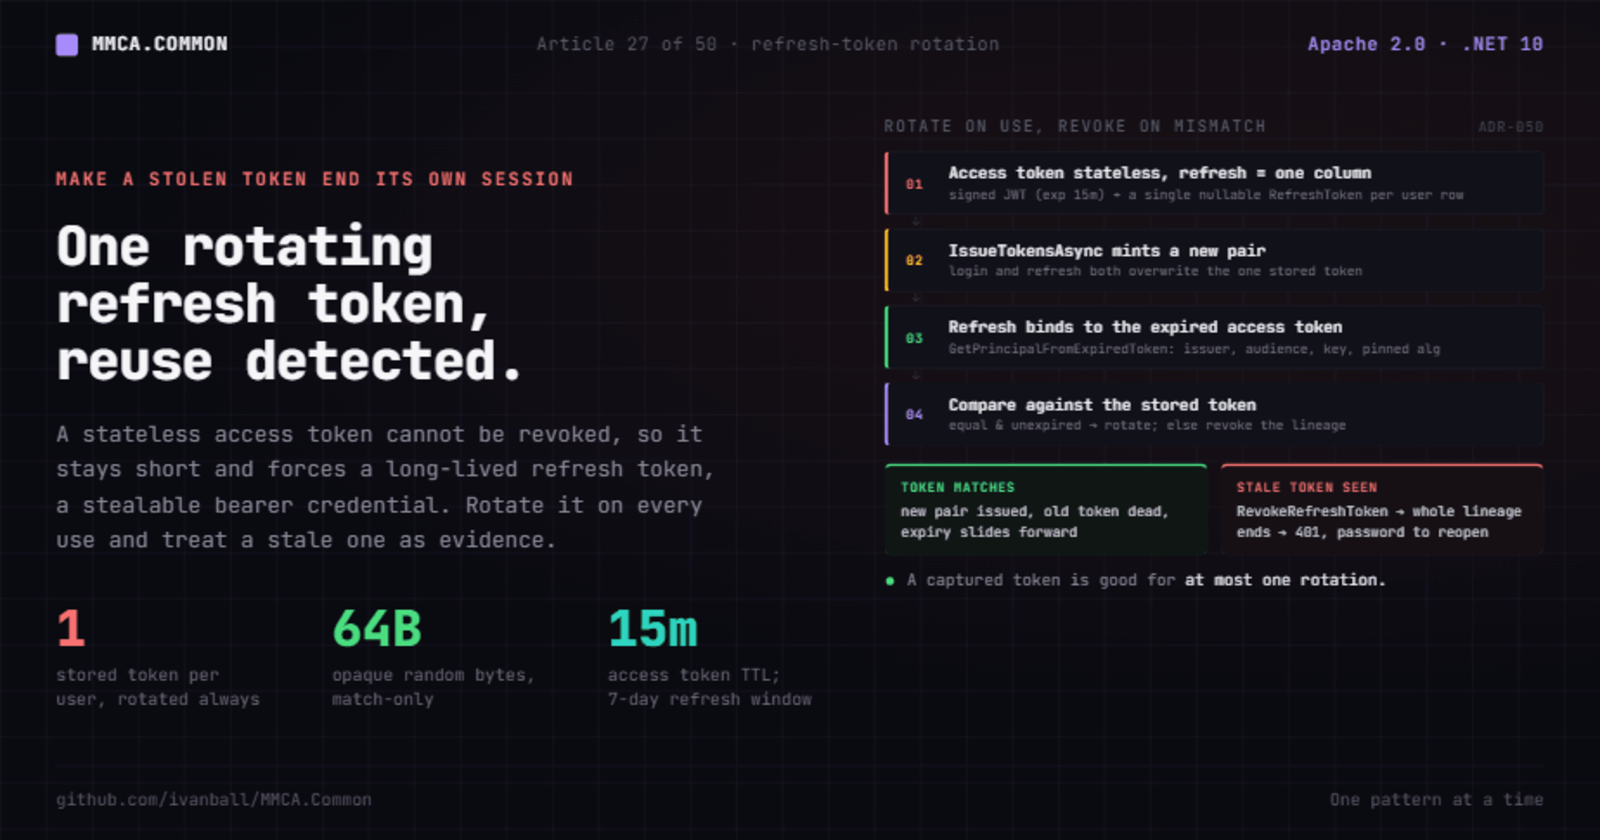
One rotating refresh token, and reuse detection that makes theft self-limiting
Medium Issue #513
A stateless JWT you cannot revoke has to be short-lived, which forces a refresh token, which is a long-lived bearer credential that can be…
-

API Gateway Patterns in ASP.NET Core: Building Scalable Microservices with YARP
C# Corner Issue #512
Build scalable microservices with ASP.NET Core and YARP. Centralize routing, auth, and more with a powerful API Gateway.
-
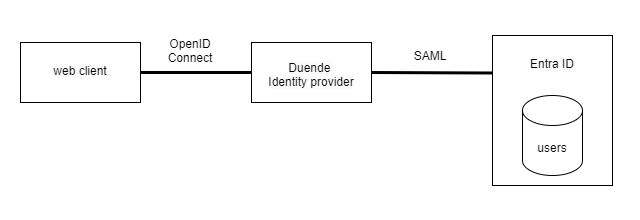
Implement SAML as an external provider in an ASP.NET Core Identity application using Duende as an OIDC server
Software Engineering Issue #511
This article shows how to implement a SAML federation from an ASP.NET Core Identity application using Sustainsys.Saml2.AspNetCore2. Entra ID is used to implement the SAML authentication and the users ...
-
Building Production-Ready MCP Servers in ASP.NET Core 10
C# Corner Issue #510
Build secure, scalable, and production-ready MCP servers in ASP.NET Core 10. Learn best practices for AI integration, authentication, and deployment.
-
MCP Security Best Practices: Authentication, Authorization, and Secure Tooling
C# Corner Issue #509
Secure your .NET MCP implementations with best practices for authentication, authorization, and tool design to protect AI integrations and enterprise data.
-
Securing ASP.NET Core APIs with Microsoft Entra ID Authentication
C# Corner Issue #508
Secure ASP.NET Core APIs with Microsoft Entra ID. Learn authentication, configuration, and best practices for robust API security.
-
OAuth 2.1 Authentication in ASP.NET Core APIs: A Practical Guide
C# Corner Issue #507
Master OAuth 2.1 for ASP.NET Core APIs. Learn PKCE, JWT validation, refresh tokens, and best practices for secure API authentication.
-

Password hashing done right: PBKDF2-SHA512, 600k iterations, timing-safe
Medium Issue #504
Storing a password is a solved problem, and almost every breach headline is someone who solved it the wrong way. Here are the four…
-

Cross-service auth without a shared secret: JWKS dual-fetch
Medium Issue #502
When you split a monolith into services, the easy answer is to copy the JWT signing secret into every validator. That is also the answer…
-
Implementing Passkey Authentication in ASP.NET Core Applications
C# Corner Issue #502
Implement secure, passwordless passkey authentication in ASP.NET Core. Leverage FIDO2 & WebAuthn for enhanced security and user experience.
-
How does your domain know your user?
Medium Issue #498
Almost every business application needs to answer a question that sounds simple: who is the current user? But “user” isn’t one thing…
-
How to Secure APIs with OAuth 2.1 and OpenID Connect
C# Corner Issue #498
Secure your APIs with OAuth 2.1 and OpenID Connect. Learn about authentication, authorization, JWTs, PKCE, and best practices for modern applications.
-

Identity API Endpoints in ASP.NET Core: When to Use Them (.NET 10)
codewithmukesh Issue #497
MapIdentityApi gives you register, login, and refresh for free in .NET 10. Here is exactly when to use Identity API endpoints and when to roll your own.
-
Static Web Apps CLI: local authentication emulation with ASP.NET
I CAN MAKE THIS WORK Issue #492
The Static Web Apps CLI has a local authentication emulator. This is a useful tool for local development, and can be used with ASP.NET authentication. This post shows how.
-
How to Implement Passkey Authentication in ASP.NET Core Applications
C# Corner Issue #491
Implement secure passkey authentication in ASP.NET Core apps. Enhance security & user experience with WebAuthn & FIDO2.
-
How Hidden Security Vulnerabilities Turn Into Business-Critical Incidents in Modern Applications
Medium Issue #490
Security is a board-level concern. IBM’s latest breach report puts the global average cost at $4.4 million per incident ($10.22 million in… Continue reading on Emerline Tech Talk »
-

AI Security Testing: How to Validate Prompts, Models, and Tool Calls
C# Corner Issue #489
Secure your AI systems! Learn to validate prompts, models, and tool calls for LLMs, RAG, and agents in .NET.